Jdscarlett27

vip
Active for: 2.5y
Peak Tier 3
No content yet
Attackers say they want 10,000 BTC from Revolut after a fake government email
Revolut has not confirmed that demand
Systems weren’t hacked, funds weren’t touched
🧵🧵🧵
post-image
BTC-3.83%
Gm legends 🧘‍♂️
CLARITY Act got a rewrite on Friday
And almost nobody’s talking about the part that actually matters
Senate Republicans published a revised 630 page draft September 10, four days before the vote
Lummis says it carries over 100 changes requested by Democrats
The real story is buried in one section
Section 20209, the DeFi rulebook, grew from 285 words to about 2,200
Here’s what it actually does
Validators, node operators, anyone publishing wallet software, get a full carve out from the Commodity Exchange Act
Never touch a private key, you’re not legally running an exchange, that
NODE+0.25%
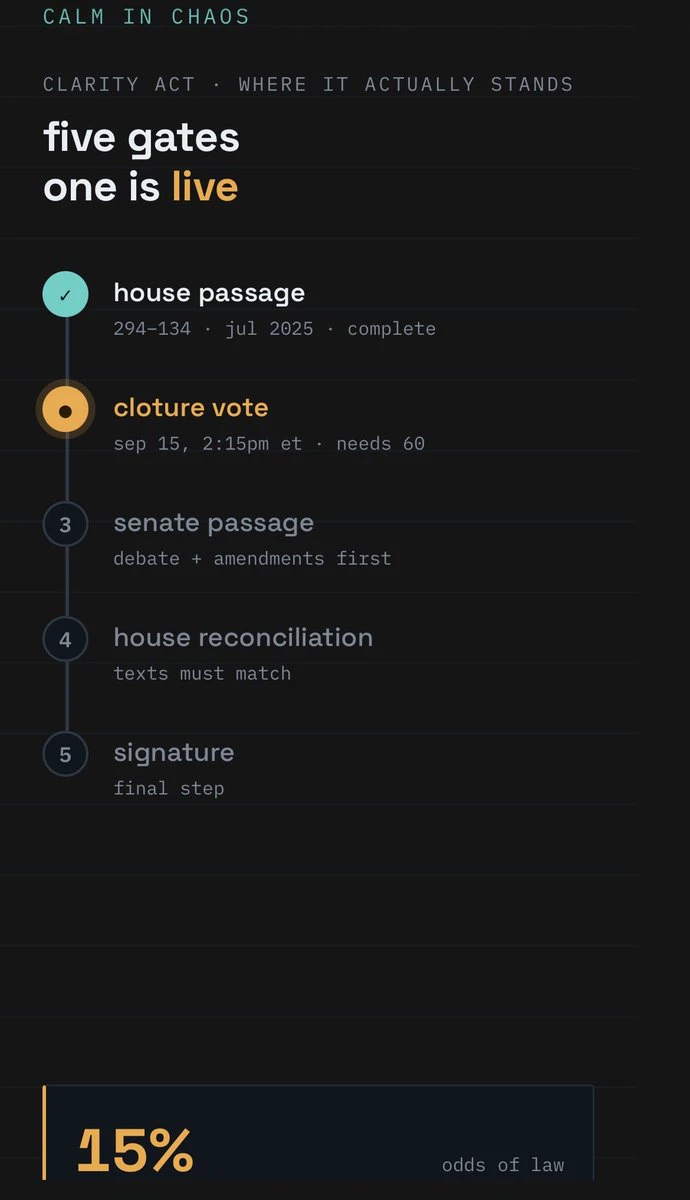
The Clarity Act update, here’s exactly where it stands
August 8, Thune filed cloture on the motion to proceed, locking in a vote date before the senate left for recess
That’s still the last official legislative action taken
September 15, 2:15pm et is the next event, a cloture vote on the motion to proceed
Not a passage vote, a 60 vote test just to start debating the bill
Republicans hold 53 seats, they need at least 7 democrats or independents to even open the door
Three fights are still blocking that number
Ethics rules bar officials and spouses from issuing or sponsoring digital assets while
post-image
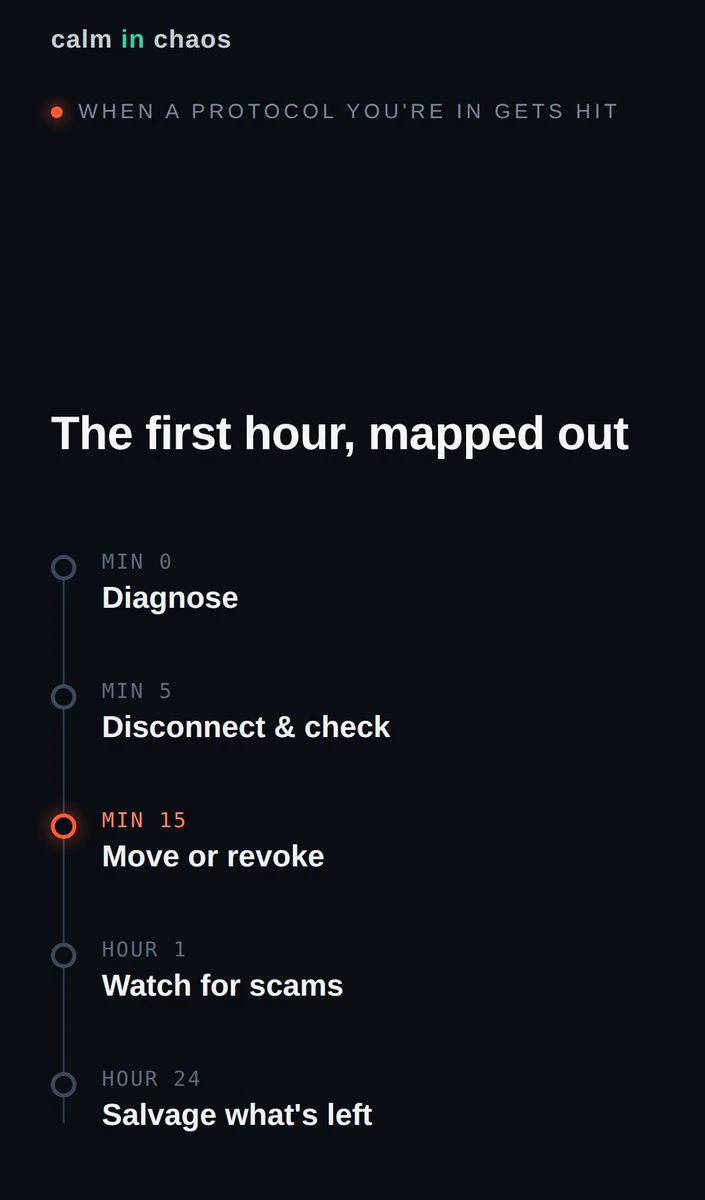
A protocol you’re in just got exploited
What you do in the next hour matters more than anything you read after
Save this before you need it
🧵🧵🧵
post-image
4,000 bitcoin left Liquid Network’s reserve yesterday
320 million dollars
The people who took it left one on-chain message
we are whitehats, contact us on chain
🧵🧵🧵
post-image
BTC-3.83%
Gm legends 🧘‍♂️
Welcome to a new week of countless possibilities
post-image
Gm legends 🧘‍♂️
How is your weekend going so far?
post-image
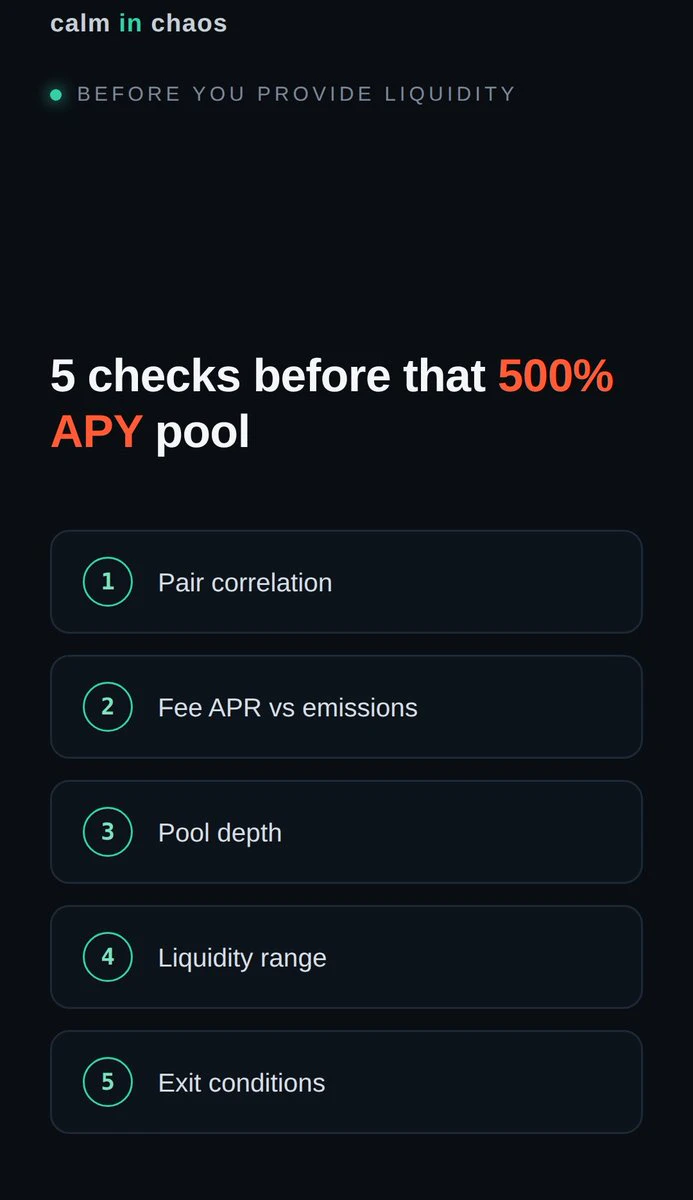
Before you chase the next 500% APY pool
Run these checks first
Because the highest APY is often where the risks people ignore are hiding
Save this one before you deposit
🧵🧵🧵
post-image
Gm legends 🧘‍♂️
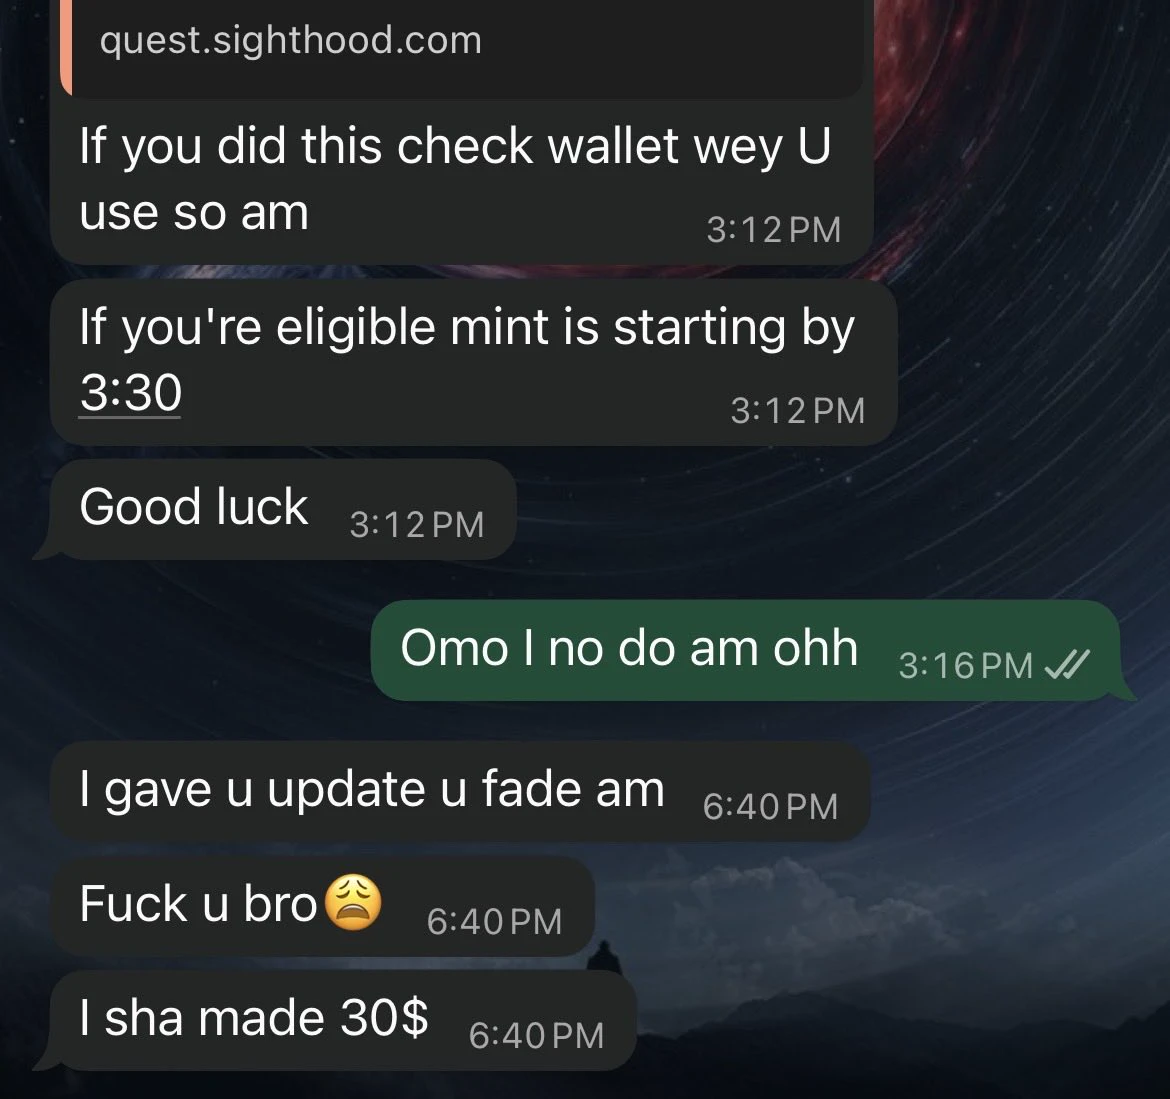
Seems like NFTs are finally back for real
And sadly that’s the 3rd one I’ve faded
At this point I need to lock in properly
Can’t keep watching the alpha pass me by 😭
post-image
  • 1
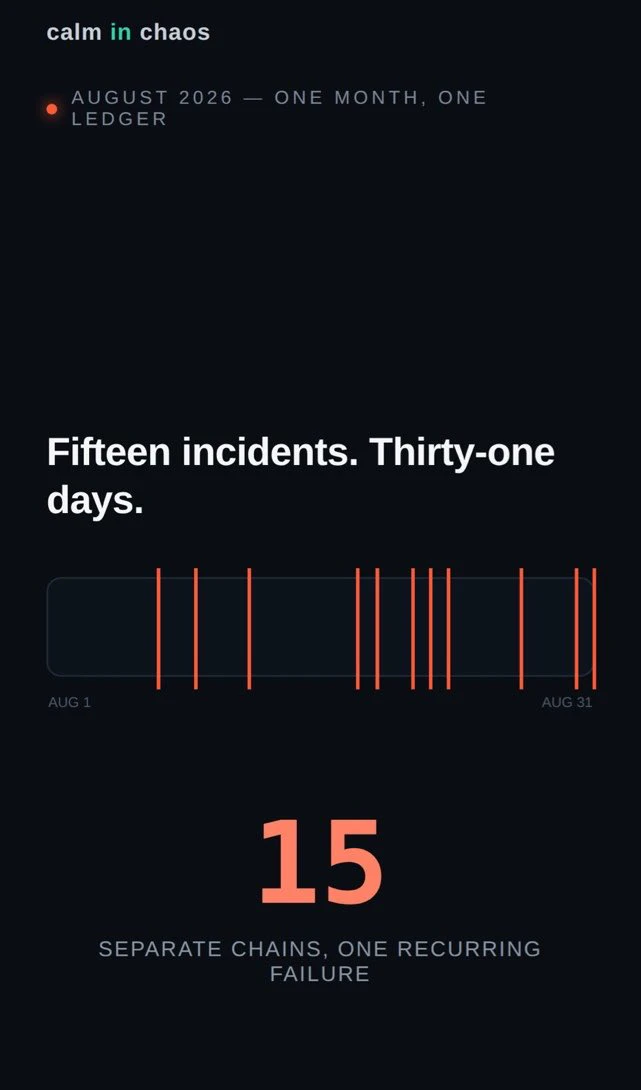
August 2026, one month, not one incident
A near-split
A three-day reorg
A 3 trillion token mint
A six-bug drain
A stolen mint role
A vote that passed because nobody showed up
Different chains
Same break
The ledger said one thing
Reality said another
🧵🧵🧵
post-image
TOKEN-4.48%
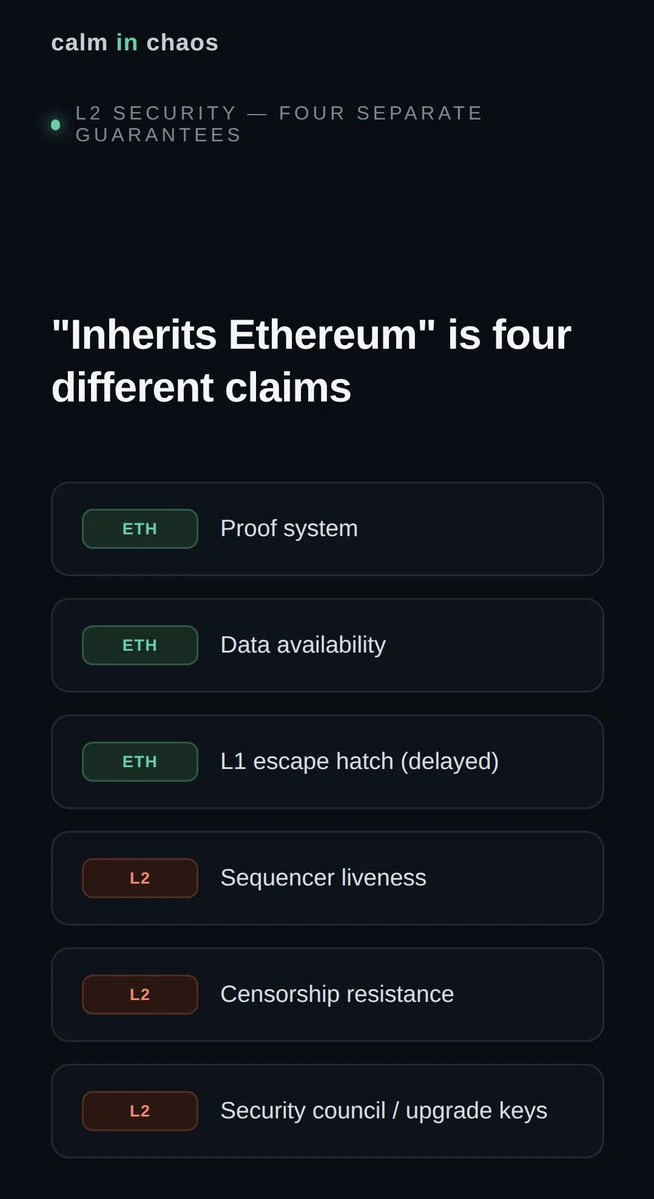
L2s inherit Ethereum’s security gets repeated like a fact
It’s not false
It’s incomplete
Here’s the part that gets left out
🧵🧵🧵
post-image
ETH-5.51%
@walsxbt Gm legend
I can feel it too 🧘‍♂️
Gm legends 🧘‍♂️
Every new day comes with its own new opportunities
post-image
Gm legends 🧘‍♂️
Term Labs lost 8.5 million yesterday and nobody broke a single line of code
The attacker didn’t find a bug they found silence
Term’s vaults run veto based governance meaning proposals pass automatically unless someone actively votes to stop them
No objection within the window equals approval
The attacker deposited a tiny stake, in some vaults barely worth a dollar, into low turnout vaults where nobody else was voting
Zero competition meant that tiny stake was effectively 100 percent of the vote
First move wasn’t the drain, it was disabling the 7 day safety delay so nobody had
post-image
ETH-5.51%
USDC+0.06%
Gm legends 🧘‍♂️
The sandbox just proved a hard truth about cross chain bridges
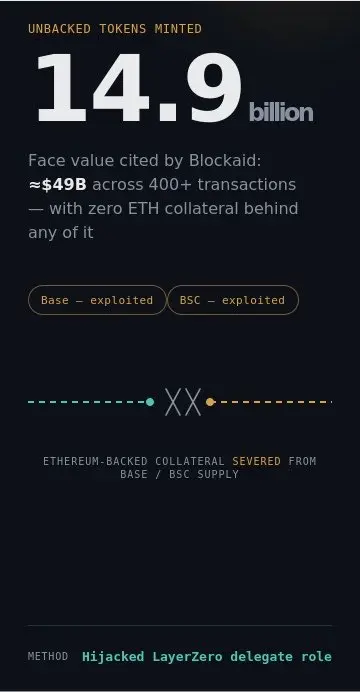
Attacker hijacked layerzero delegate permissions on sand’s omnichain token contract on base
Used a function called approveandcall to bypass minting controls entirely
Billions in unbacked sand minted out of thin air on base and bnb chain
No wallet hacked
No private key stolen
Just a permission nobody was watching closely enough
🧵🧵🧵
post-image
SAND-6.61%
ZRO-1.28%
Let’s break down what actually happened because the headlines are messier than the mechanism
Sandbox’s sand token uses an omnichain fungible token setup through layerzero
This lets sand move between ethereum base bnb chain and polygon
Each chain has a delegate role controlling minting permissions
SAND-6.61%
ZRO-1.28%
ETH-5.51%
BNB-1.49%
Blockaid flagged it first around 04:14 utc
Attacker hijacked the delegate role on base and used approveandcall to mint sand with no eth backing behind it
Face value minted hit roughly $49b across 400+ transactions
Peckshield separately tracked 14.9b sand minted across two addresses at 05:40 utc
SAND-6.61%
ETH-5.51%
Here’s the detail most posts are missing
Blockaid clarified this is not a layerzero bug
The flaw sits in sandbox’s own oft contract on base
Approveandcall let the attacker call setdelegate and mint through a forged lzreceive
Layerzero’s own contracts behaved exactly as designed
Know the difference between protocol risk and app level config risk
It changes who needs to fix what
ZRO-1.28%
SAND-6.61%
Sandbox confirmed at 07:22 utc
Vulnerability identified and fully contained
Real impact under 0.01% of total sand supply
Eth and polygon sand unaffected
No user wallets compromised
Eth locked backing for all bridged sand fully intact
SAND-6.61%
ETH-5.51%
Immediate response
Bridging to and from base and bnb chain disabled
Sand on both networks isolated can’t be moved or redeemed
Users told plainly don’t buy sell or trade sand on base or bsc
A pre incident snapshot was taken
Compensation plan in prep for qualifying lp holders
Full technical postmortem still to come
BNB-1.49%
SAND-6.61%